GRC · Identity and access · Microsoft 365
IT and GRC, built hands-on.
Six years in Amazon operations taught me that a control only works when people follow it and you can prove it. Now I build the systems and the evidence.
Looking for
Entry-level roles in GRC and compliance, IT audit, Microsoft 365 administration or identity and access, in Orlando or remote. I'd especially value a team that mentors.
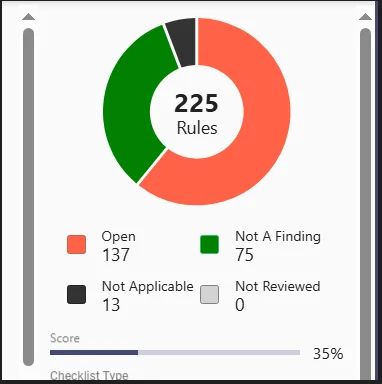
GRC Security Program
A full security program for a fictional coffee shop: risk register, 15 NIST 800-53 controls crosswalked to PCI DSS 4.0.1, an evidence pack with automated checks, a vendor risk assessment, and quarterly access reviews.
Workspace intranet
A data-driven intranet that runs identically from memory, the browser, or a real Microsoft 365 tenant — live-tenant verified, a stored XSS found and fixed across 60 sinks, 454 automated checks.
Cyber Home Lab
Entra ID and SharePoint governance built in a real Microsoft 365 tenant — then reviewed against itself, which is how I found that the audit log had never been turned on.
Also
Websites and tools for small businesses
I also build small, working things for real people. See how I work with small businesses →